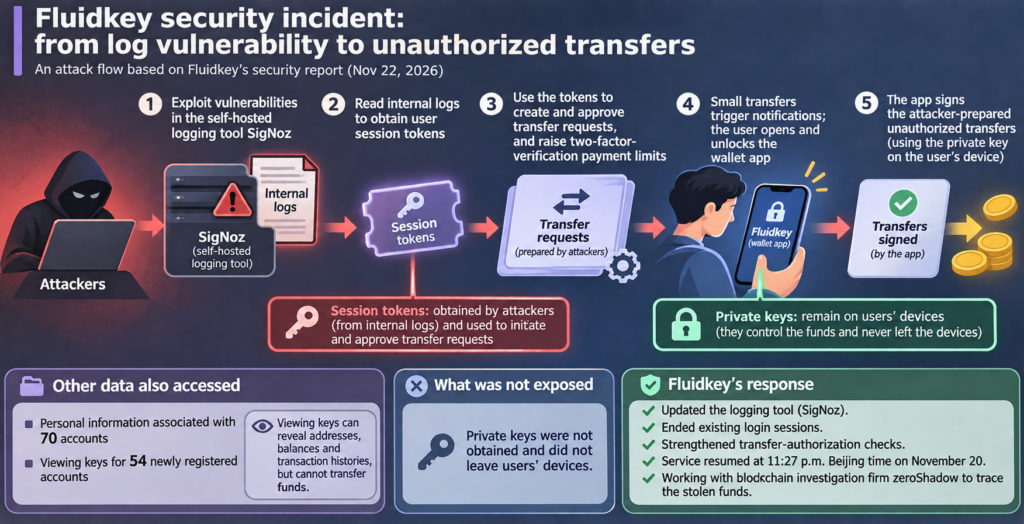
In a security report published on November 22, 2026, crypto wallet Fluidkey said attackers stole approximately $1.6 million from 52 accounts after exploiting two vulnerabilities in SigNoz, its self-hosted logging tool.
According to Fluidkey, the attackers read internal logs to obtain user session tokens. They then used those tokens to create and approve transfer requests and raise two-factor-verification payment limits. Small transfers triggered notifications; when users opened and unlocked the app, it signed unauthorized transfers the attackers had prepared in advance. Fluidkey said the private keys controlling the funds never left users’ devices.
Fluidkey also reported that some personal information associated with 70 accounts and viewing keys for 54 newly registered accounts were obtained. Viewing keys can reveal addresses, balances and transaction histories, but cannot transfer funds.
The company said it updated the logging tool, ended existing login sessions and strengthened transfer-authorization checks. It said service resumed at 11:27 p.m. Beijing time on November 20 and that it was working with blockchain investigation firm zeroShadow to trace the stolen funds.