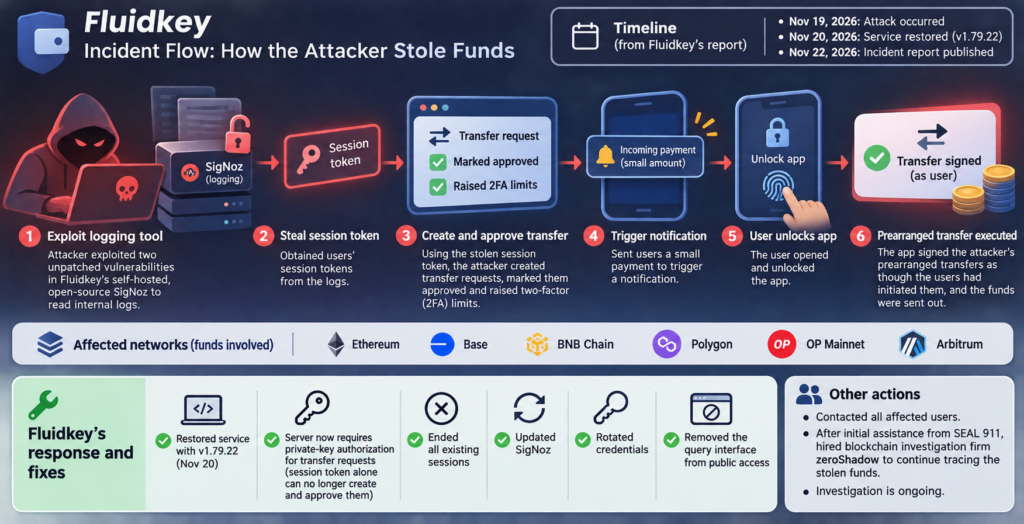
In a report published on November 22, 2026, privacy wallet Fluidkey said an attacker had stolen about $1.6 million from 52 accounts on November 19. The affected funds were on Ethereum, Base, BNB Chain, Polygon, OP Mainnet and Arbitrum. Fluidkey said its investigation was ongoing.
According to Fluidkey’s incident review, the attacker exploited two unpatched vulnerabilities in its self-hosted, open-source SigNoz logging tool to read internal logs and steal session tokens. Using those tokens, the attacker created transfer requests, marked them approved and raised two-factor limits. The attacker then sent users small payments to trigger notifications. Fluidkey said that when users opened and unlocked the app, it signed the attacker’s prearranged transfers as though the users had initiated them.
Fluidkey said it restored service with version 1.79.22 on November 20. Its server now requires a user’s private-key authorization for transfer requests, so a session token alone can no longer create and approve them. The company also ended existing sessions, updated SigNoz, rotated credentials and removed a query interface from public access. It said it had contacted all affected users and, after initial assistance from SEAL 911, hired blockchain investigation firm zeroShadow to continue tracing the stolen funds.