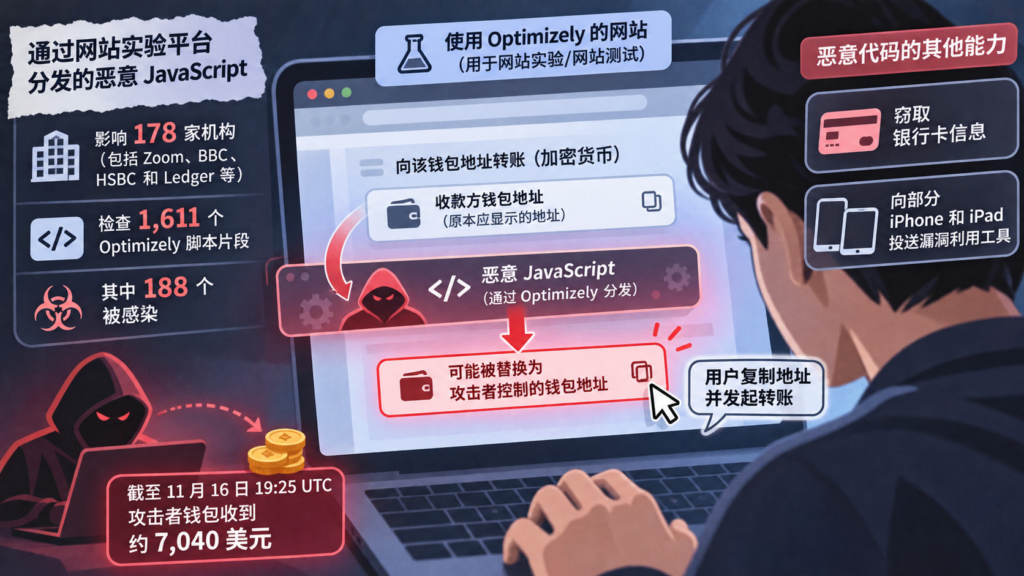
Originally reported November 17, 2026, at 07:42 (UTC+8). Security researcher Scott Helme disclosed that malicious JavaScript distributed through the Optimizely website experimentation platform affected 178 organizations, including Zoom, the BBC, HSBC and Ledger, according to 深潮 TechFlow.
Researchers examined 1,611 Optimizely script snippets and found 188 infected. The malicious code could replace a crypto wallet address shown to a user, steal payment-card information and deliver an exploit kit to some iPhones and iPads. The wallet-address capability matters because a sender could copy an attacker-controlled address instead of the intended recipient’s; the report does not establish how many payments, if any, were redirected.
As of November 16 at 19:25 UTC, the attacker’s wallet had received about $7,040. Helme said most of the malicious code had been removed, but how the attacker obtained write access remained unclear.
Source: techflowpost.com (originally published 2026-11-17 07:42 UTC+8)