Reported: November 11, 2026, 09:27 (UTC+8), by PANews, citing Cointelegraph. This is that report, not a later update.
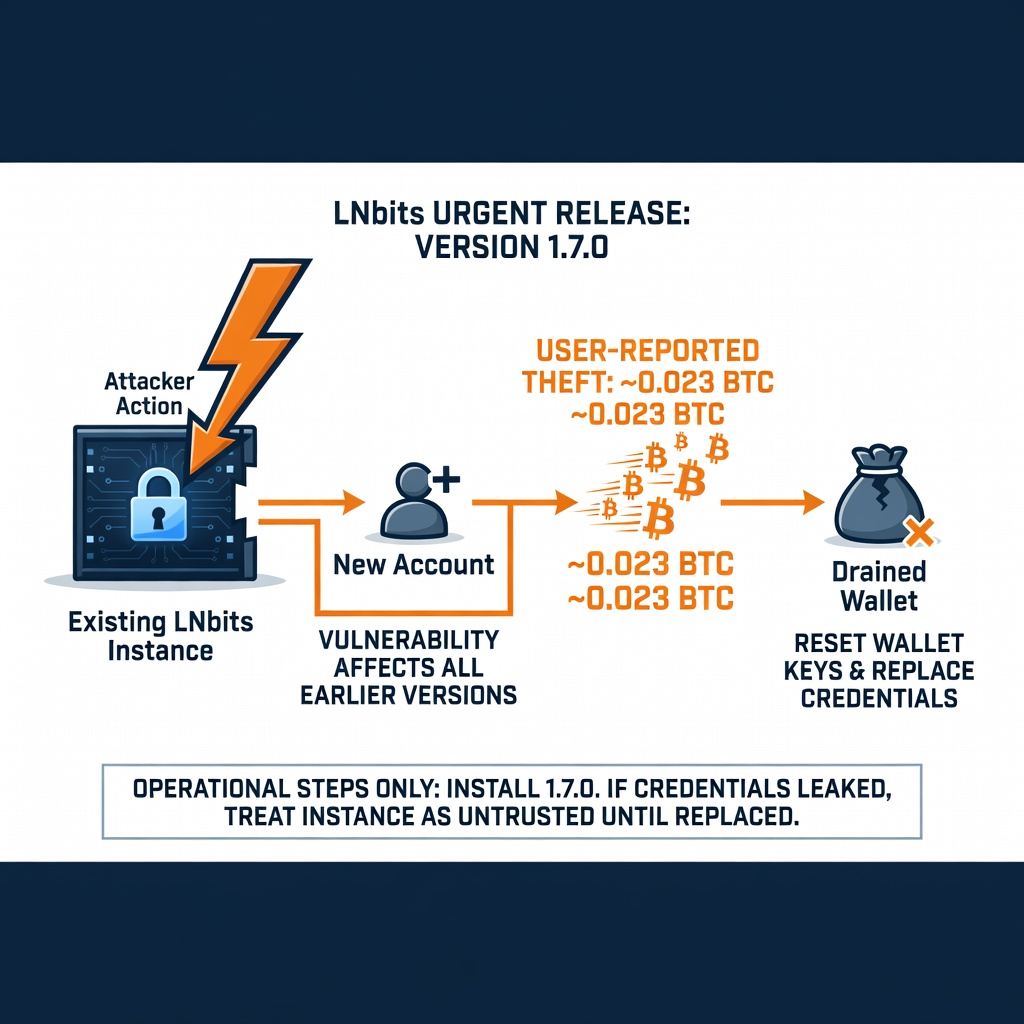
PANews said the Bitcoin Lightning wallet platform LNbits had urgently released version 1.7.0 after a recent wave of attacks that stole funds, and urged users to update immediately.
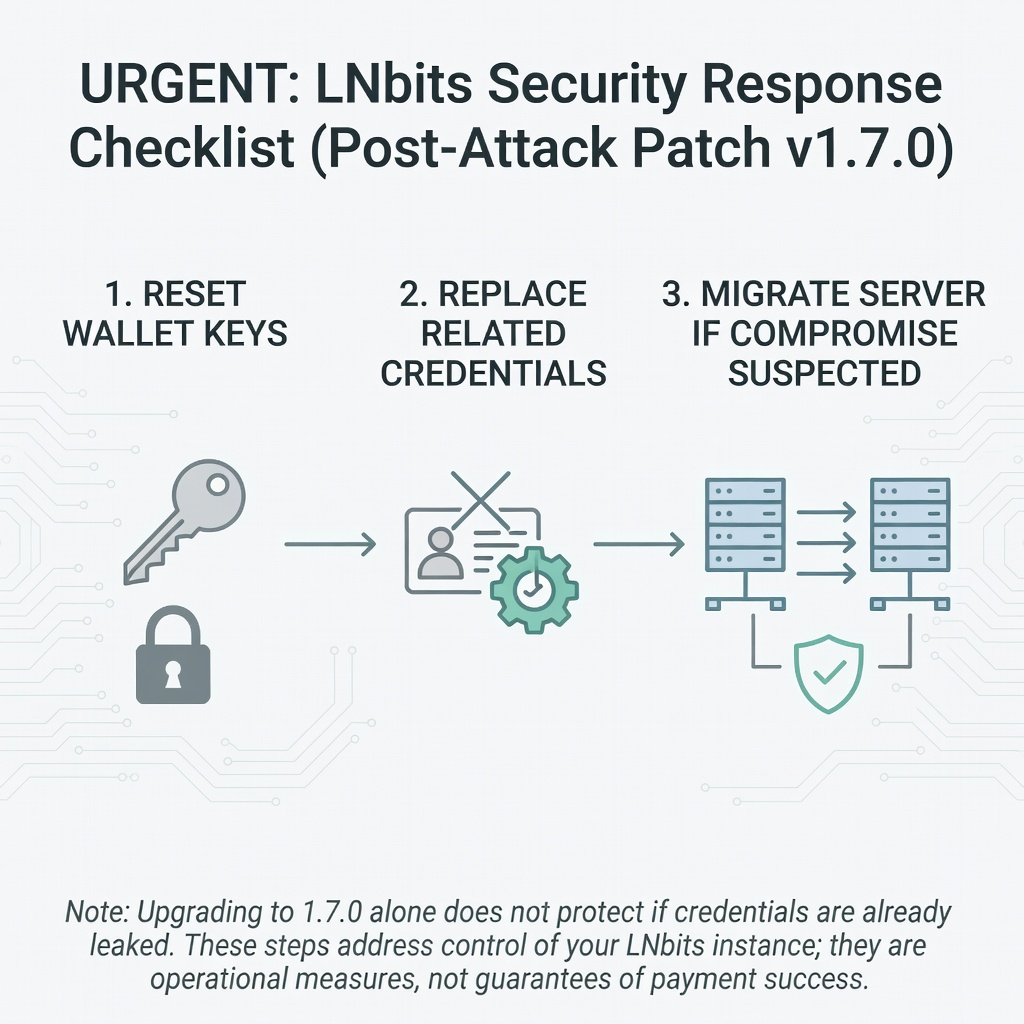
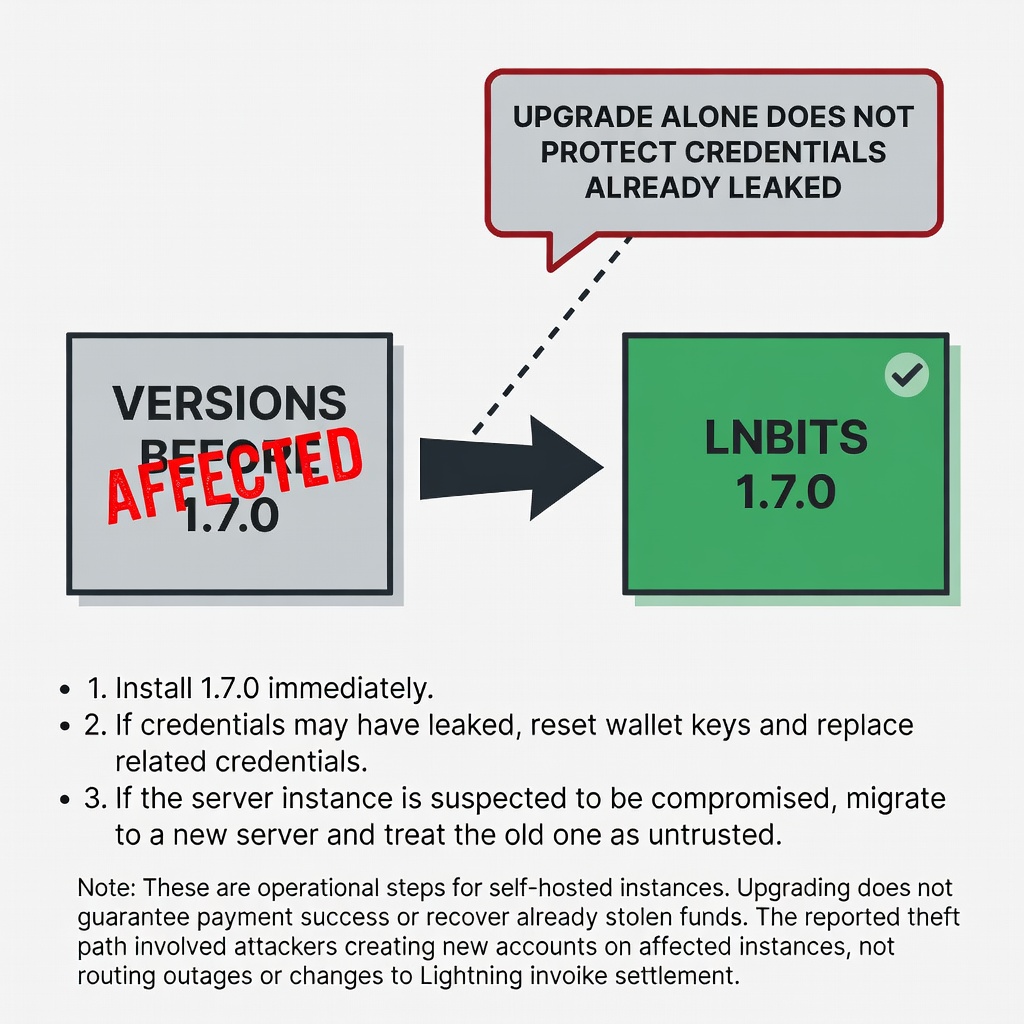
LNbits warned that the vulnerability affects all earlier versions. Upgrading alone does not protect users whose credentials have already been leaked. It advised resetting wallet keys, replacing the related credentials, and migrating the server if an operator suspects the instance was compromised.
Founder Ben Arc said that after losses to users and to the team, the team was working to respond. Some users reported that attackers used their LNbits instances to create new accounts and stole about 0.023 bitcoin.
The notice is about control of an LNbits instance and its credentials. It does not describe a routing outage, a channel-capacity limit, or a change in how Lightning invoices settle, and it does not say whether the reported bitcoin was on-chain wallet balance or Lightning channel liquidity. The only theft path it records is user reports that attackers created new accounts on affected instances.
For someone running LNbits on their own server, the stated steps are operational, not a promise that payments will then succeed: install 1.7.0, and if credentials may already have leaked, treat the wallet keys and that server as untrusted until they are replaced.
Original article: PANews, November 11, 2026